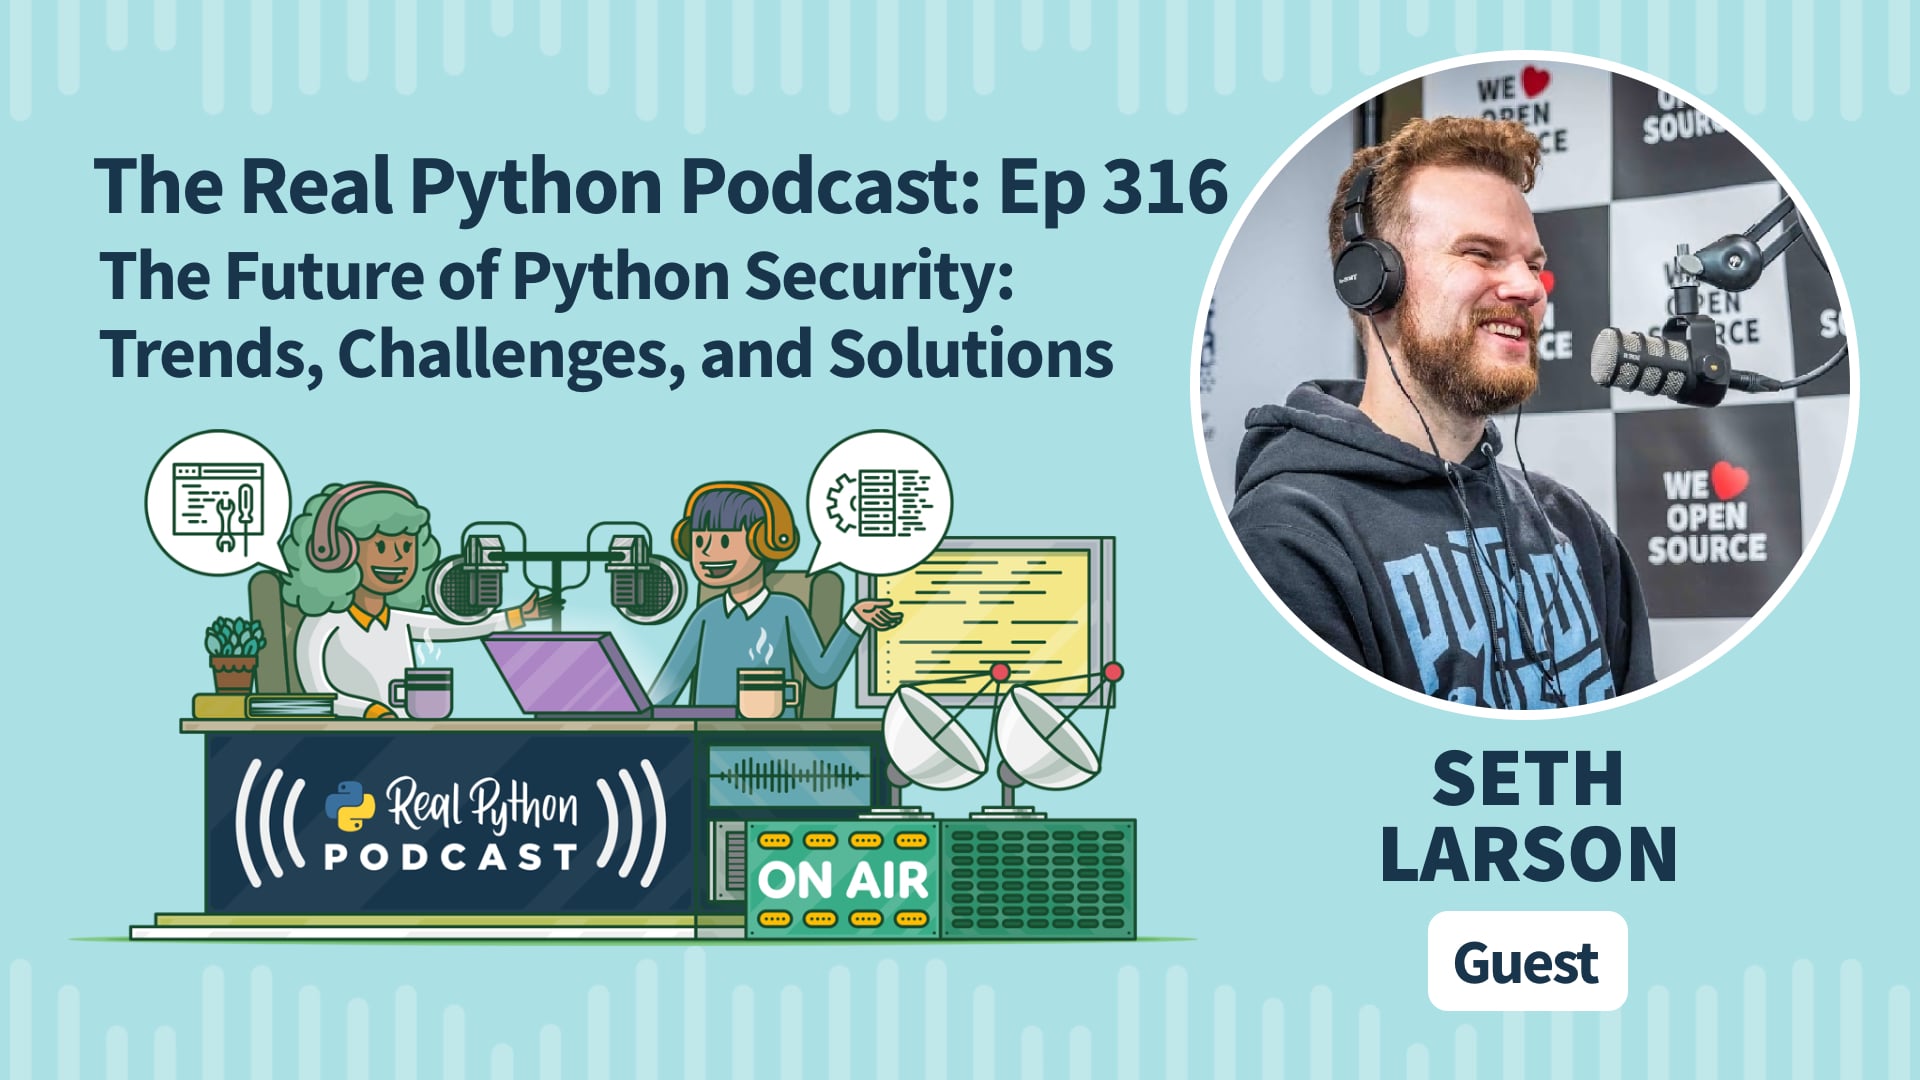
Episode 316: The Future of Python Security: Trends, Challenges, and Solutions
The Real Python Podcast
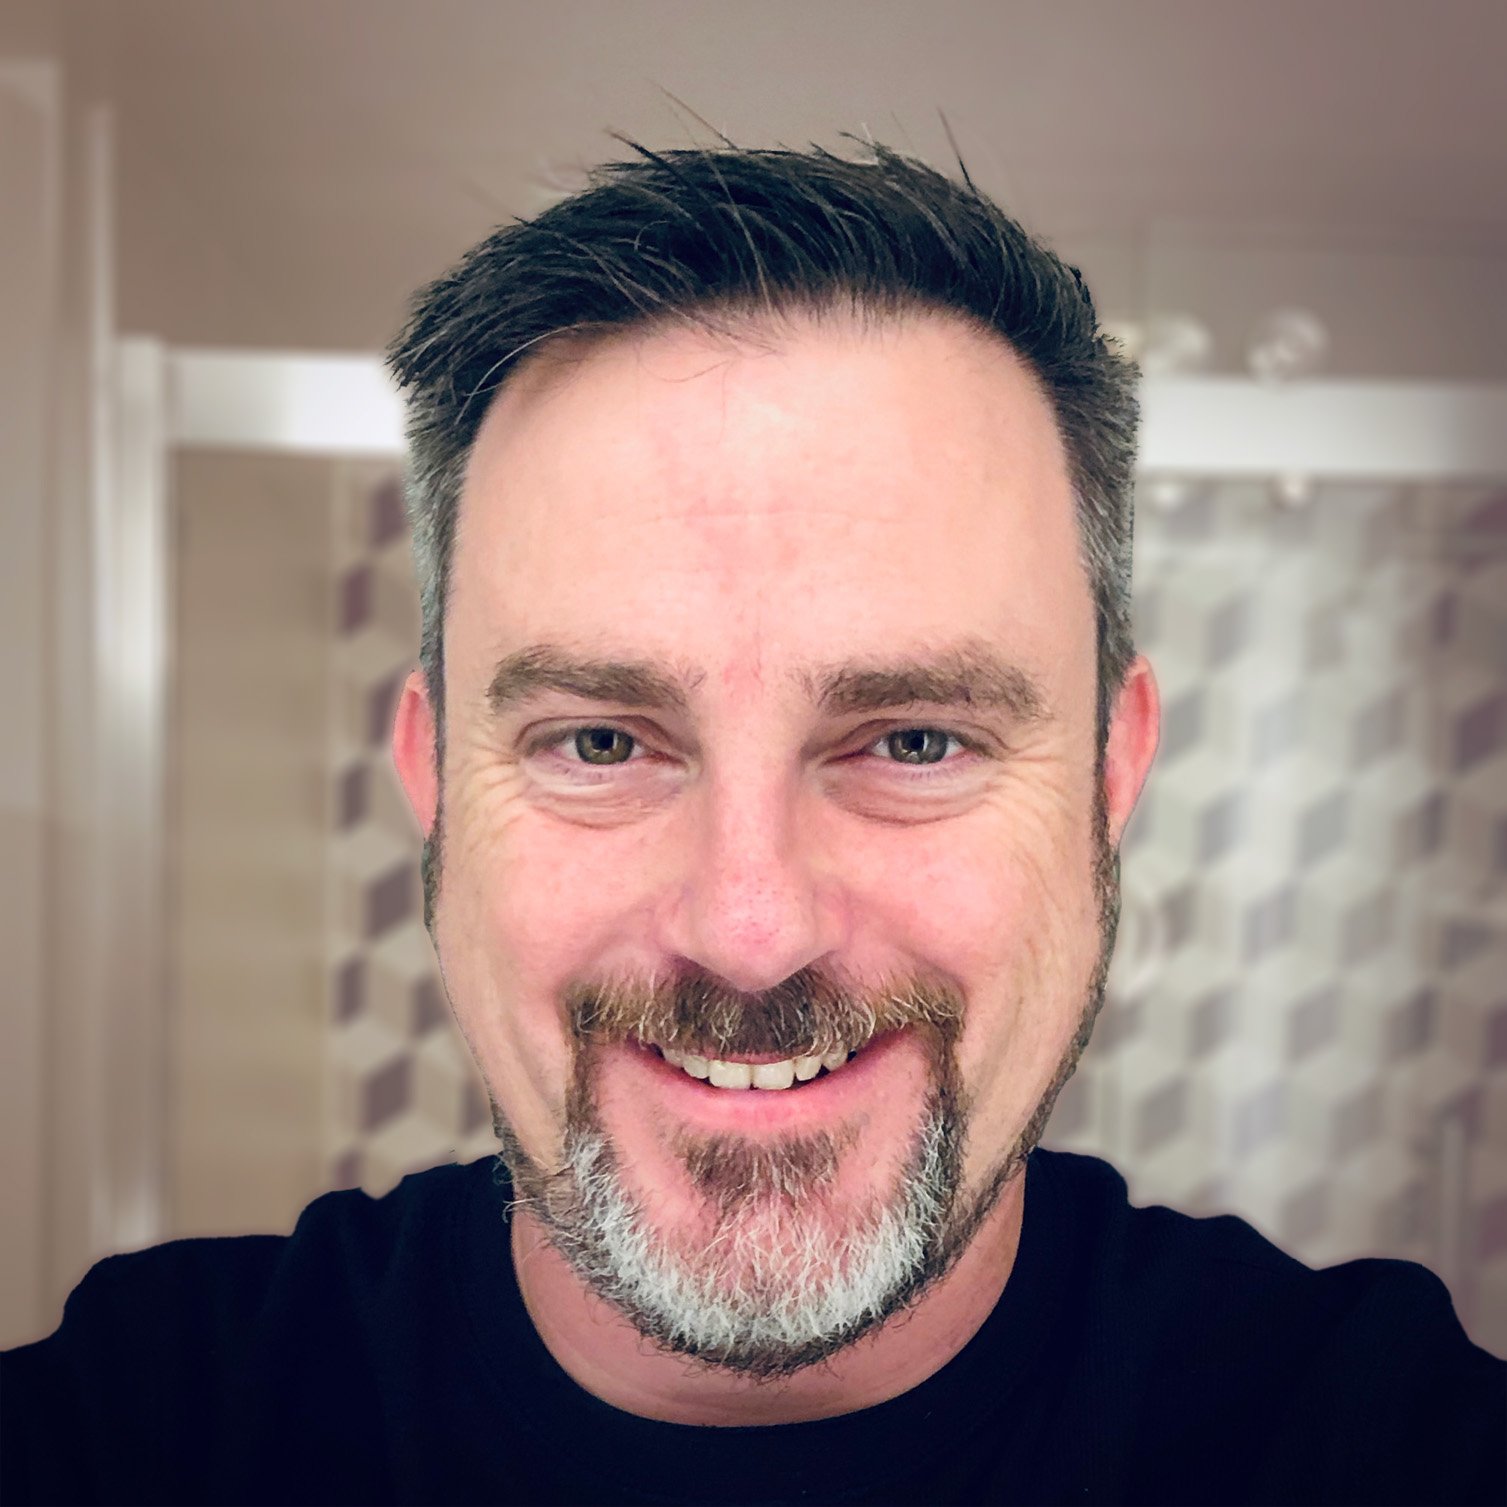
How is the Python ecosystem adapting to the modern landscape of software security and supply chain defense? This week on the show, we sit down with Seth Larson, the Python Software Foundation’s Security Developer in Residence.
Seth shares his background in open source and how he got involved in security engineering. We discuss the Python Security Response Team and how a recent PEP formalized its processes for reporting and triage.
Seth breaks down how large language models are affecting vulnerability discovery and increasing the volume to triage. We also cover the security advantages of trusted publishing on PyPI, how Software Bill of Materials (SBOMs) under PEP 770 help track dependencies, and some advice on improving your CI/CD security.
Course Spotlight: Testing Your Code With Python’s unittest
Learn how to use Python’s unittest framework to write unit tests for your code, including test cases, fixtures, and test suites.
Free Bonus: Python Security Checklist
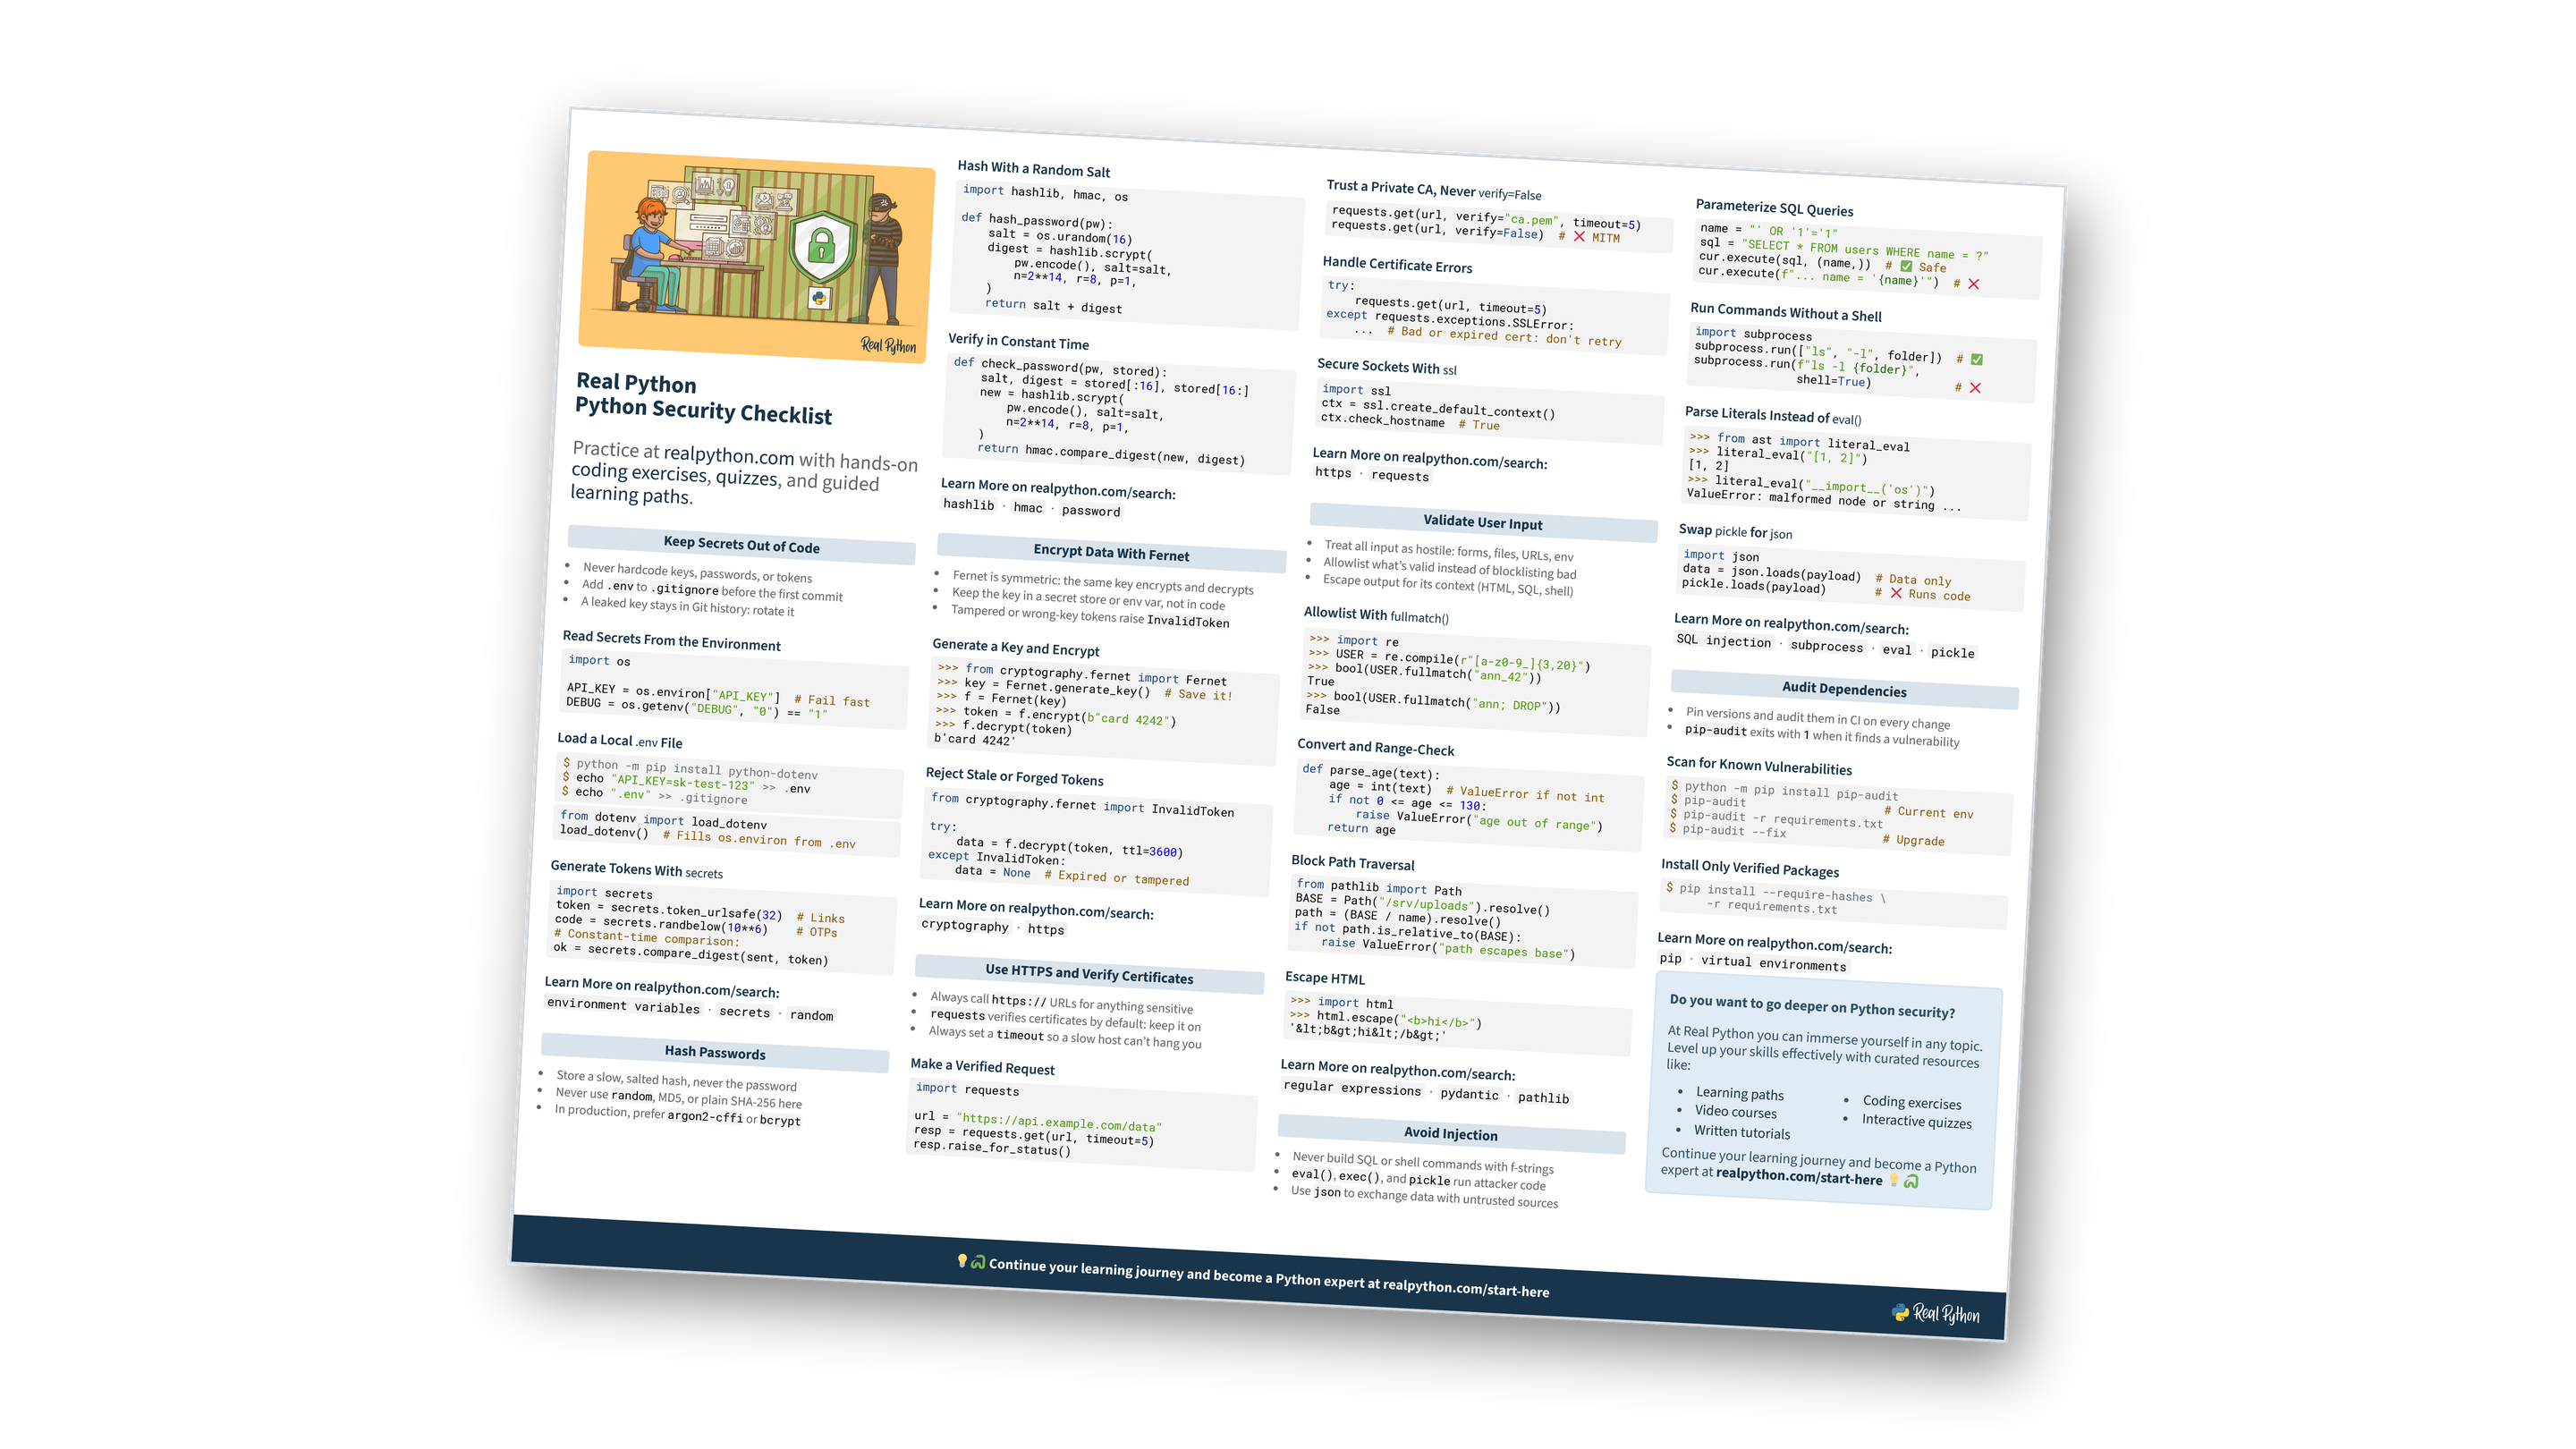
Get a Python Security Checklist (PDF) and keep secrets, passwords, encryption, HTTPS, input validation, and dependency audits on one printable page:
Topics:
- 00:00:00 – Security Note: Python certifi package and PHP updates
- 00:00:37 – Introduction
- 00:02:22 – Pikmin fans unite!
- 00:02:51 – How did you get involved in security research?
- 00:07:07 – Security Research is unique and the wider community
- 00:13:35 – The influx of LLMs finding vulnerablities
- 00:17:18 – The Python Security Response Team and PEP 811
- 00:25:21 – Video Course Spotlight
- 00:26:44 – Is the flood of vulnerabilities unlimited?
- 00:29:15 – Security Track at PyCon US 2026
- 00:31:03 – Does a security engineer need humility?
- 00:33:25 – PEP770 Improving measurability of Python packages with Software Bill-of-Materials
- 00:38:55 – Communication across other languages and package repositories
- 00:41:41 – What’s it been like writing PEPs?
- 00:44:32 – Defining the term Trusted Publisher
- 00:47:27 – Differences between public and private vulnerabilities
- 00:51:19 – Are you using LLMs in your work as a security researcher?
- 00:52:56 – The fear/hype cycle of vulnerabilites and triaging reports
- 00:58:35 – Do you have security advice for developers?
- 01:03:12 – What are you excited about in the world of Python?
- 01:06:14 – What do you want to learn next?
- 01:08:08 – How can people follow your work online?
- 01:09:58 – Thanks and goodbye
Show Links:
- Seth Larson - Website
- Removal of emSign root cerificate - Advisory - certifi/python-certifi
- Supply Chain Security for the Age of AI-Speed Exploits – Real Python
- urllib3 - PyPI
- PSF Developers in Residence - Python.org
- Keynote: Security Work isn’t Special - Seth Larson - OpenSSF Community Day
- Phantom Dependencies: is your requirements.txt haunted? - Seth Michael Larson - YouTube
- PSF - Update from our Security Engineers - YouTube
- Python Security: What we’ve done, now AI & Glasswing are changing everything (Sponsor: Alpha-Omega) - YouTube
- Learning from the not-so-secret Python security “cabal” - Seth Michael Larson - YouTube
- PEP 811 – Defining Python Security Response Team membership and responsibilities
- PEP 770 – Improving measurability of Python packages with Software Bill-of-Materials
- PEP 770 Software Bill‑of‑Materials (SBOM) data from PyPI, Fedora, and Red Hat — Seth Larson
- Trusted Publisher - Getting Started - PyPI Docs
- zizmor: Static analysis for GitHub Actions (and more)
- Pikipedia, the Pikmin wiki
- Rust for CPython (Python Language Summit 2026) | Python Insider
- Python Software Foundation News
- Python Insider
- Seth Larson - Website
Want to go deeper on this episode? Mentor AI can explain the topics it covered and find tutorials to learn more.
Ask Mentor AI